DigiCert Chief Trust Officer On How CAs and Auditors Can Avoid an eMudhra-Like Incident
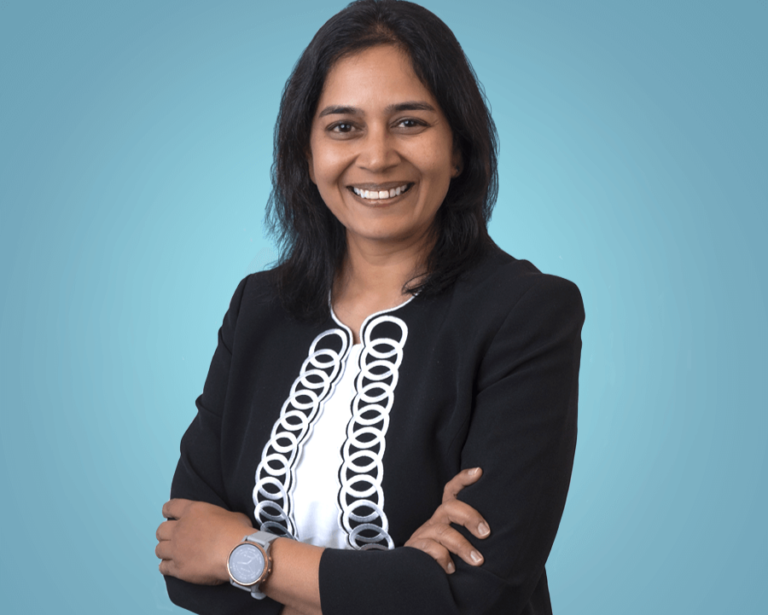
Lakshmi Hanspal, Chief Trust Officer, DigiCert explains why the eMudhra incident occured last month, and suggests preventive measures and auditing process refinements.
- Prevention requires strong controls across the entire cryptographic lifecycle.
- Key generation, transfer and deployment should follow independently reviewed procedures, with strict change controls, separation of duties and verification before any issuing certificate authority becomes trusted.
- A certificate authority should confirm that every key it publishes is generated securely, tested for strength and verified for usage.
- Independent auditors in India should apply the same rigorous technical scrutiny expected of auditors anywhere in the global public trust ecosystem.
eMudhra, a Bengaluru-based certificate authority trusted by every major browser, had the private keys of eight of its certificates exposed in October 2026. With those keys, anyone could create a valid-looking certificate for any website, including your bank, your email or a government portal. What’s more, nobody noticed this slip-up for 18 months. And it passed two audits without the slip-up being detected.
While Google, Mozilla, Apple and Microsoft moved within days to block the certificates, eMudhra’s shares fell by a fifth in a single day. eMudhra has since exited its global business of issuing security certificates for websites.
In an email interview, we asked Lakshmi Hanspal, Chief Trust Officer, DigiCert for the details and how such incidents can be avoided in future.
DigiCert is a global leader in intelligent trust. It protects more than 125,000 organizations, including 90% of the Fortune 500, by ensuring the security, privacy and authenticity of every interaction.
Edited excerpts follow:
How can such security incidents be prevented in future?
Prevention requires strong controls across the entire cryptographic lifecycle. Certified hardware is essential, but the procedures and software surrounding it must be equally rigorous.
Key generation, transfer and deployment should follow independently reviewed procedures, with strict change controls, separation of duties and verification before any issuing certificate authority becomes trusted. In eMudhra’s case, its published incident report describes a custom key-handling script that weakened keys after they were initially generated correctly.
A certificate authority should confirm that every key it publishes is generated securely, tested for strength and verified for usage. That underscores why organizations must verify the outcome of a process, alongside the equipment used.
Organizations also need to prepare for urgent certificate replacement. A complete inventory, clear ownership and automation that can replace and deploy certificates on demand can help prevent a provider incident from becoming a business outage. Routine renewal automation alone does not establish that readiness.
What changes are needed in validation processes?
The validation process has to move from trusting a ceremony to proving its output. Validation should cover the full path from key generation to the certificate ultimately published and used. Teams should verify that the certified public key matches the approved key generated in the secure environment, and repeat those checks after any transfer or transformation. Custom scripts and exceptions to standard procedures deserve independent technical review and testing before use.
It is also important to distinguish customer identity and domain validation from validation of a certificate authority’s own cryptographic controls. The disclosed failure concerned CA key handling. Stronger identity checks alone would not have prevented it. The priority should be demonstrable key integrity, secure handling and evidence that every critical step operated as intended.
What do independent Indian auditors need to do?
Independent auditors in India should apply the same rigorous technical scrutiny expected of auditors anywhere in the global public trust ecosystem. Auditors should verify what a certificate authority actually produced, witness key ceremonies and sign off on the verified results. They should examine whether controls work in practice through direct evidence: key ceremony records, hardware configurations, execution logs, script reviews, and reconciliation of generated keys with published certificates. A hardware certification or documented procedure should be a starting point for examination.
eMudhra has stated that the affected hierarchy passed two independent audit cycles. That warrants a careful review of audit scope, the evidence examined, and why the weakness escaped detection. Auditors should bring specialist cryptographic expertise into these engagements, scrutinize procedural exceptions and verify remediation through follow-up testing. Findings and limitations should be communicated clearly to the relevant oversight bodies and browser root programs.
Controller of Certificate Authorities (CCA regulator) should update audit criteria to require output verification and ceremony witnessing.
How is DigiCert helping organisations prepare for a post-quantum future?
We help organisations turn quantum risk into an actionable security programme. The starting point is understanding where cryptography is used, what it protects, and which dependencies will make migration difficult. DigiCert Quantum Central brings together cryptographic inventory data, applies organisational policies, and helps teams prioritise remediation, assign ownership, and track progress. That gives security leaders a way to demonstrate measurable improvement across a complex, multiyear transition.
We also help organisations prepare for deployment through PKI modernisation, certificate lifecycle automation, and tools for testing and integrating post-quantum cryptography. Our guidance is to begin with a critical environment, assess compatibility, and adopt supported protections in stages. Protecting sensitive network traffic against “harvest now, decrypt later” risks is one practical starting point.
From a trust perspective, the goal is lasting cryptographic agility: knowing what needs to change, having accountable owners and being able to make that change safely as standards and threats evolve.
How does the DigiCert Partner Network, built on DigiCert ONE, help partners address immediate certificate lifecycle needs and expand into broader trust engagements?
The immediate priority is business continuity: knowing where certificates are, who owns them and how to replace them before services are disrupted. DigiCert Trust Lifecycle Manager (TLM) gives partners the capabilities to discover certificates, apply consistent policies and automate issuance, renewal and deployment. That helps customers address urgent replacement needs and manage shorter certificate lifespans.
These same capabilities are essential to quantum readiness. Organisations need to understand where certificates and their underlying cryptography are used, identify what must change and automate replacement as post-quantum standards and supporting technologies are adopted. TLM helps establish that visibility and operational control, building the cryptographic agility needed to migrate safely and at scale.
For partners, certificate management becomes the starting point for a broader engagement: modernising legacy PKI, strengthening governance and preparing customers for cryptographic change.
Through the wider DigiCert ONE portfolio, they can extend those services to software integrity, device identities, content provenance and trust for AI models and agents. The value is a sustained relationship that meets immediate operational needs while preparing the customer’s trust infrastructure for the future.